TL;DR
- CraftForms never shows a CAPTCHA. Instead, every form quietly watches how it was filled in: mouse movement, focus events, keystrokes vs. paste, and how naturally the timing plays out.
- A submission that doesn’t look human — no mouse movement, no focus, no typing, filled out far faster than a person physically could — gets blocked right there in the browser, with a plain “Spam submission detected” message. No redirect, no lecture, no “prove you’re not a robot.”
- A real visitor who interacts with the form at all — clicks a field, types a character, even just engages with the submit button — never comes close to being flagged. The check is invisible to them by design.
- I run this on several of my own WordPress sites, including my highest-traffic one, and haven’t had a single spam submission come through since turning it on. That’s not a lab result — it’s just what’s happened in production.
- Being honest about the limits: this is a client-side heuristic, not a server-side firewall. It’s a very effective first line of defense against the form-spam bots that actually exist in the wild — but it isn’t the same claim as “unbeatable,” and this post says so plainly.
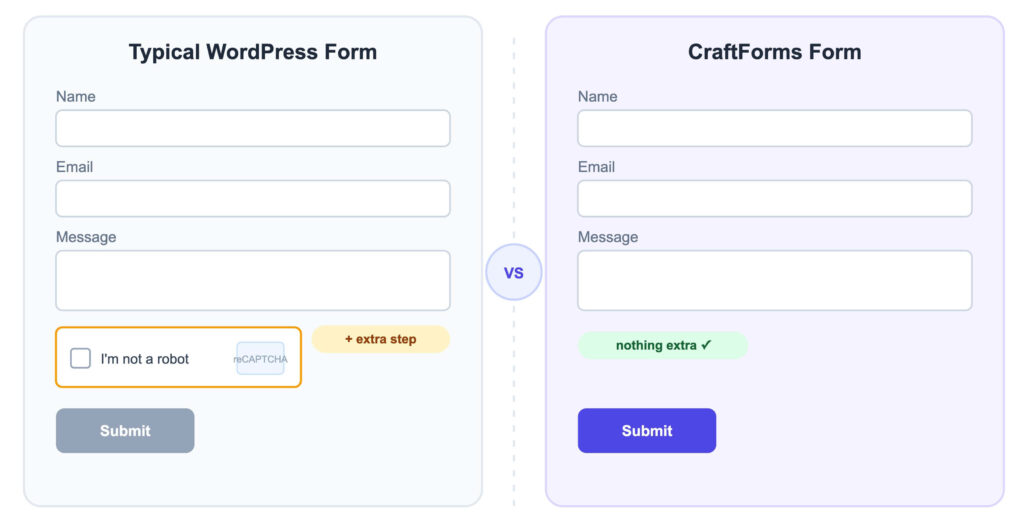
If you’ve ever added a CAPTCHA to a WordPress form, you already know the trade-off nobody advertises: it stops some bots, and it also makes some real visitors leave. Google’s own reCAPTCHA v2 checkbox occasionally escalates into a grid of blurry street signs. Mobile users hate it. Screen-reader users have a genuinely bad time with it. And you’re trusting a third-party script with performance and privacy implications, just to protect a contact form.
CraftForms takes a different bet: don’t ask the visitor anything. Watch how the form actually gets filled in, and let the behavior answer the question instead.
How spam bots actually fill out a form
Almost every automated form-spam tool — from a crude script to a headless-browser bot — shares a set of tells, because they’re optimizing for volume, not for looking human:
- They don’t move the mouse. There’s no pointer to move; the values are set directly.
- They don’t focus fields in sequence. A human tabs or clicks through a form field by field; a bot just writes into the DOM or POSTs a payload.
- They don’t type. Values appear instantly — either injected all at once, or dumped in via a single paste-like operation.
- They’re fast. A form that takes a human 20–60 seconds to read and fill gets “submitted” in under a second by a script, sometimes before the page has even finished rendering.
None of that requires a CAPTCHA to detect. It just requires paying attention.
What CraftForms actually watches
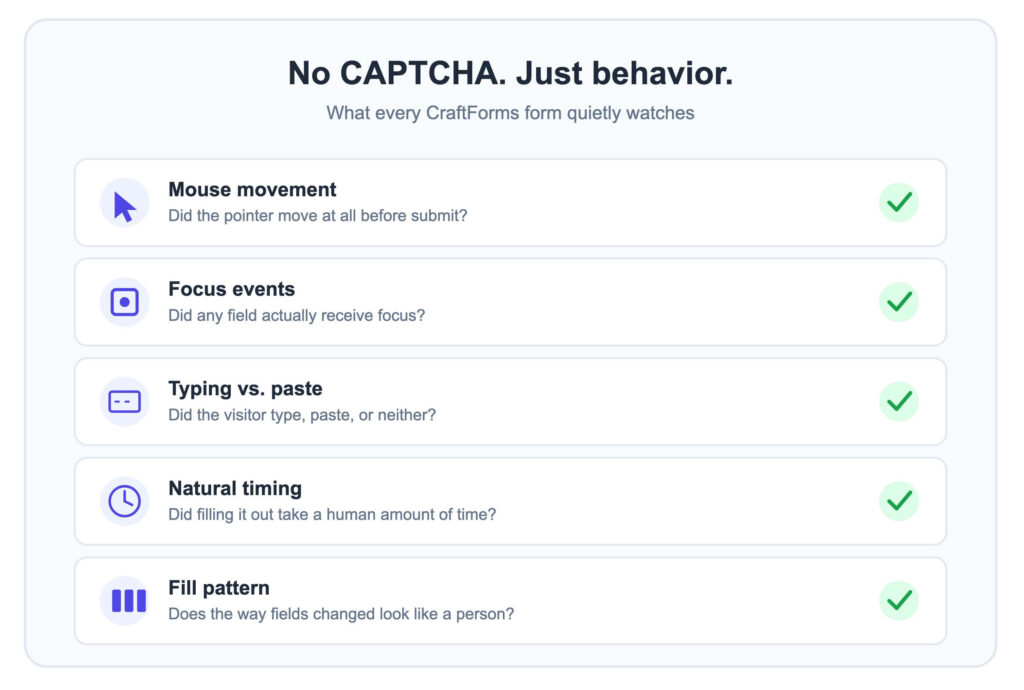
Every CraftForms form tracks a handful of signals for the life of that page load — all client-side, all invisible, nothing rendered on screen:
- Mouse movement — did the pointer move at all?
- Focus events — did any field actually receive focus?
- Keystrokes vs. paste — did the visitor type, paste, or neither?
- Timing — how long between the form appearing and the submit firing, and did submit happen before the form had even finished rendering?
- Input-change pattern — a lot of fields changing with very few keystrokes typed looks like autofill or a scripted fill, not a person.
CraftForms also accounts for legitimate edge cases a naive detector would punish — like a form with sensible defaults already filled in, where a real visitor just glances at it and clicks submit without typing anything. Genuine physical interaction with the form is always read as a human signal, however it shows up.

The score, and what crosses the line
Each of those signals feeds into a single behavioral score for the submission, weighted by how strongly it points to “not human.” No single signal is treated as proof on its own — it’s the combination that matters, which is exactly why a person absent-mindedly filling out a form never gets close to a false positive, while a script that never touches the page like a human does trips several signals at once, immediately.
Cross the threshold, and the submission gets blocked right there in the browser, before it’s ever sent to the server. The visitor (or, more accurately, the bot) sees a plain “Spam submission detected.” message. Nothing about the score, the breakdown, or the mechanism is exposed anywhere in the page — the internals aren’t something we publish, for the same reason a lock manufacturer doesn’t publish pin depths.
A real person filling out a real form essentially never triggers this. They move the mouse. They click into a field. They type something, even one character. Any one of those alone rules out an entire category of “this looks like a bot.”
Real-world results: I run this on my own sites
I don’t just build this — I use it. I manage several WordPress sites that run CraftForms, including my main site, which gets a meaningful amount of traffic. Every one of them uses this exact behavioral check, with no CAPTCHA anywhere in the form. Since turning it on, none of them has received a spam submission. Not “spam is down” — zero.
I’d rather be precise than impressive here: this isn’t a controlled study, and I’m not claiming it stops literally every bot that could ever exist. It’s a report from actually running the thing, on real forms, exposed to real internet traffic, for a while now.
Being honest about what this is — and isn’t
This is a genuinely useful post specifically because it doesn’t oversell the mechanism, so here’s the honest version:
-
It’s a behavioral check, evaluated as the form is filled out. A basic spam bot that fills a visible
<form>— which describes the overwhelming majority of what actually hits WordPress sites — never gets past it, because it never produces human-shaped behavior in the first place. - It’s not a substitute for edge-level protection. It’s not a WAF, and it doesn’t claim to be. If you’re running a very high-traffic, public-facing form that you expect to become a specific target — not just incidental spam traffic — pair this with protection at the edge (Cloudflare Turnstile, a security plugin’s rate limiting, or your host’s WAF). CraftForms’ behavioral check is the friction-free first layer, not the last line of defense for a form under active, targeted attack.
For the form volume most WordPress sites actually deal with — generic spam bots crawling for any submittable form — this is the whole story, and it’s the reason you can skip the CAPTCHA entirely.
Try it
There’s nothing to configure. Every CraftForms form ships with this on by default — no toggle to find, no threshold to tune, no third-party script to add. Install CraftForms, build the form, publish it — the spam filtering is already running before you’ve thought about it once.
Summary
- CraftForms scores form submissions using behavioral signals — mouse movement, focus, keystrokes vs. paste, and timing — entirely in the browser and entirely invisible to the visitor.
- Cross the threshold and the submission is blocked before it’s ever sent, with a plain message; nothing about the scoring mechanism is ever shown.
- Legitimate edge cases — like a form with sensible defaults where someone just clicks submit — are accounted for, so real visitors are never unfairly penalized.
- In real production use across several of my own sites — including my highest-traffic one — this alone has kept spam at zero.
- It’s a behavioral first layer, not a server-side firewall: excellent against the generic bots that make up most form spam, but pair it with edge-level protection on a form under deliberate, targeted attack.